nexbaseSOLID BASE, INFINITY CARE Book a demo
NexControl · Monitoring · Security · Compliance

Your whole SAP landscape on one screen.

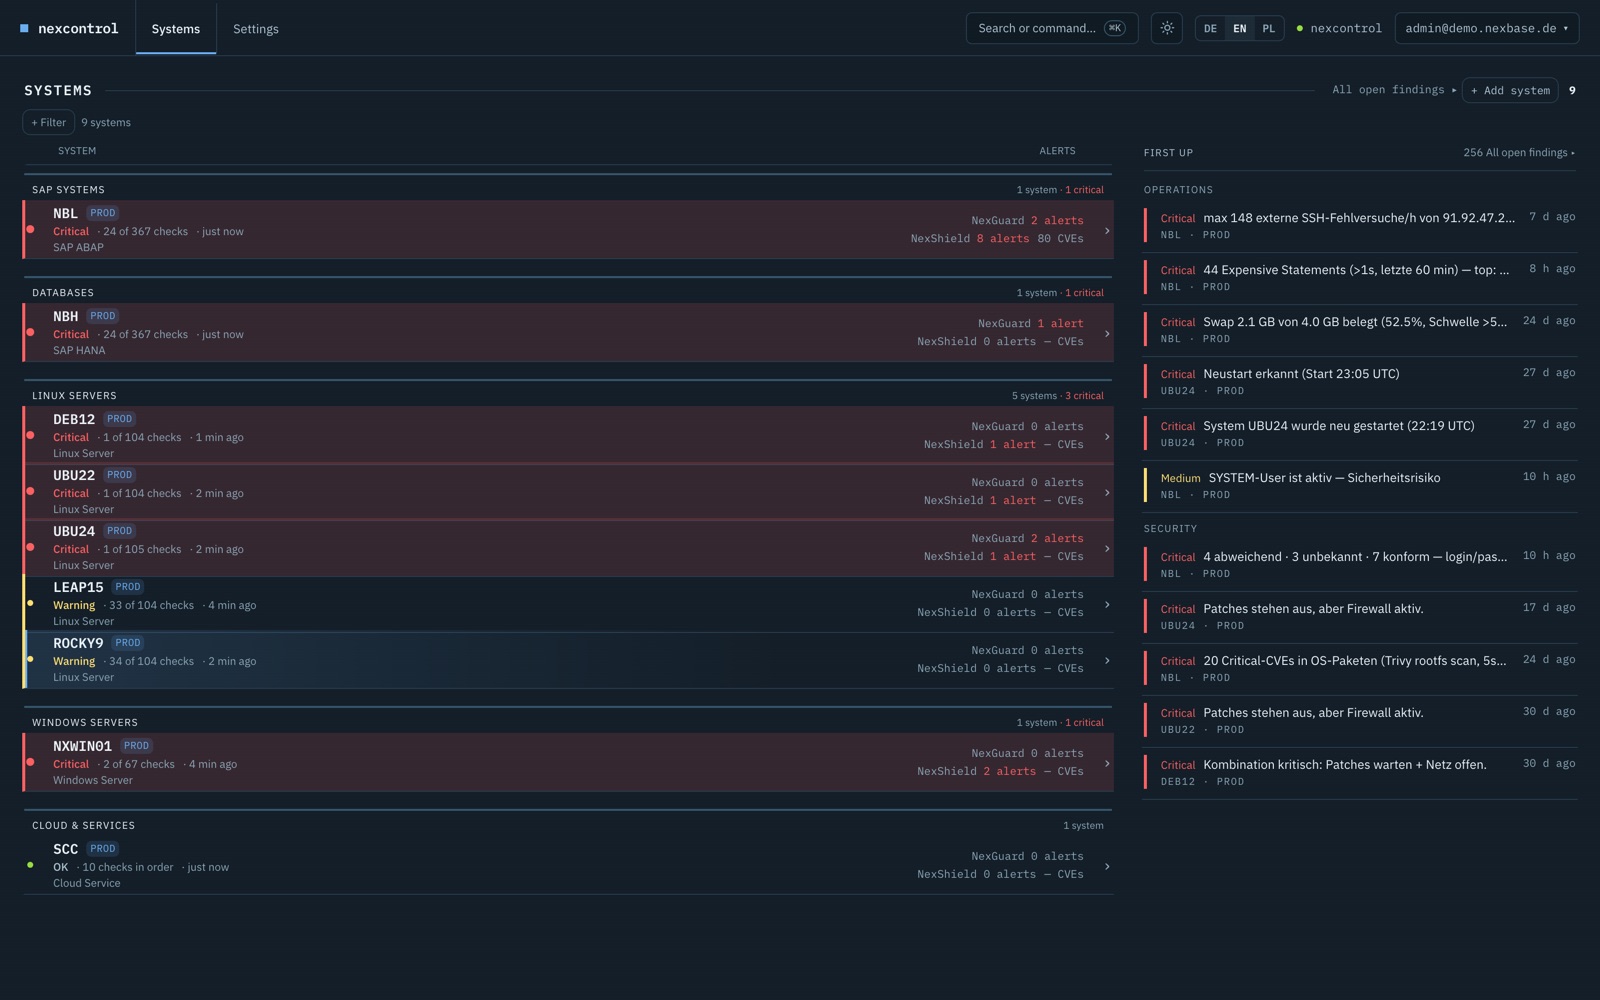
One agent, 367 checks per SAP system: NexControl also monitors HANA, Linux and Windows servers and SAP cloud services (Cloud Connector, BTP, CPI), finds vulnerabilities and turns measurements into audit-ready evidence for NIS2, ISO 27001 and national frameworks. Built by us, with an interface in English, German and Polish.

NexControl interface: monitored SAP, HANA, Linux and Windows systems with status and alerts
367checks per SAP system
SAP · HANA · Linux · Windowsplus cloud services: SCC, BTP, CPI
EUhosted with data in the EU
DE · EN · PLinterface in three languages
Products

Three tools, one set of data.

The same agent delivers monitoring, security and compliance – no further tool and no separate data import needed.

NexGuard

Monitoring

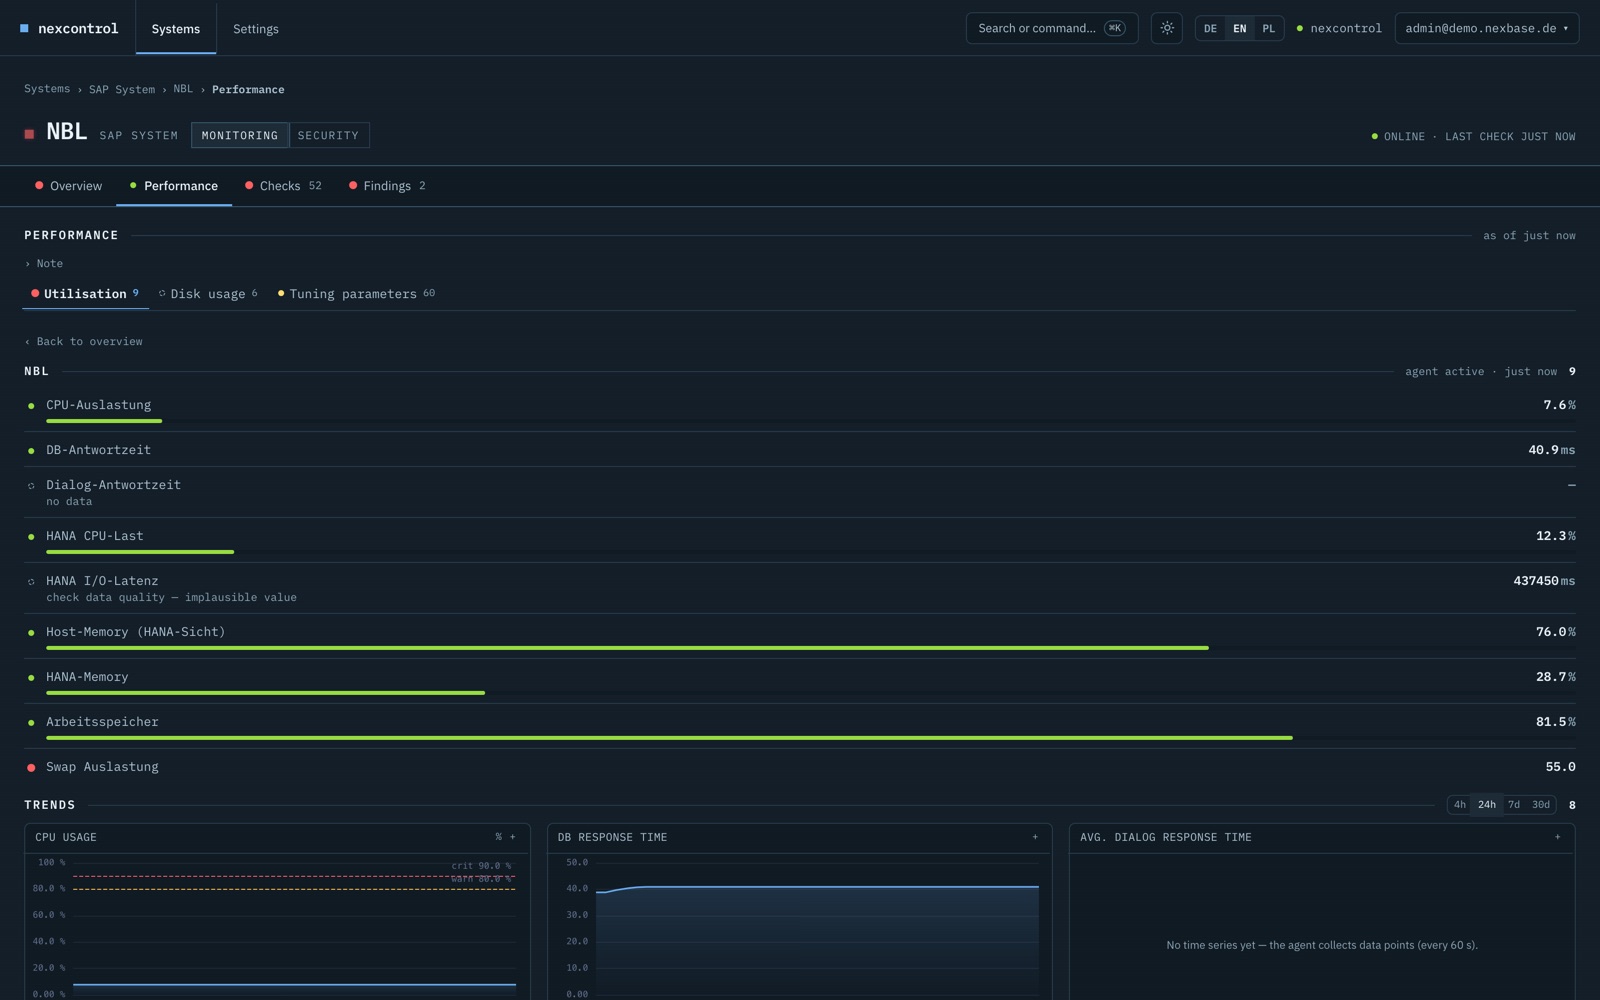
Measures every minute: processes, jobs, backups, response times, disks, HANA memory and certificate lifetimes. On deviation an alert arrives by e-mail or Microsoft Teams – with the cause and transaction code, not just a red light.

Thresholds adjustable per system; maintenance windows without false alarms.
NexShield

Security

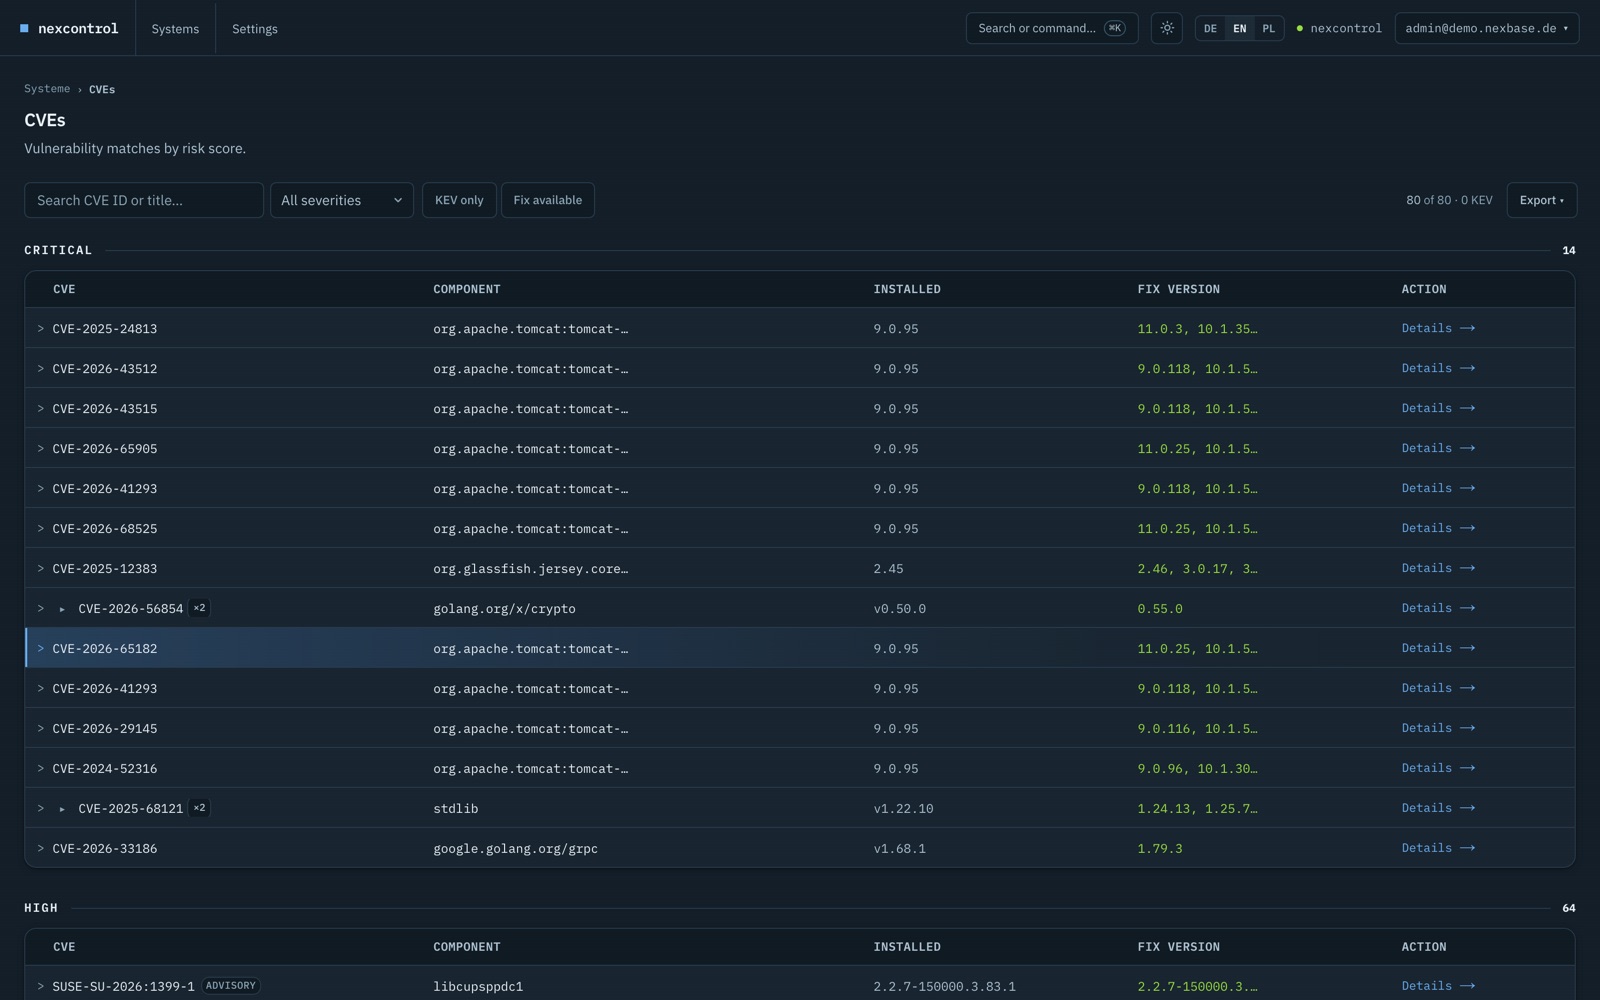
Checks hardening and vulnerabilities: standard users, gateway ACLs, audit log, profile parameters, plus a daily comparison of installed packages against known CVEs. Every finding names the fix.

Ranked by exploitability, not just by score.
Compliance

Evidence

Maps measurements and findings to 14 standards – NIS2, ISO 27001 and national frameworks for Poland and Germany. Shows per control: proven, open or not measured.

One piece of evidence counts towards several standards.
Together

From alert to evidence

An example: the agent measures failed SSH logins, NexShield turns them into a finding with source IPs, Compliance records the remediation as evidence. The same measurement answers all three questions.

Every step logged so it holds up in an audit.
Monitoring view with live measurements and history curves
Security view: vulnerability hits ranked by risk
Scope

What exactly is checked.

The full structure of the platform: monitoring areas, security checks and compliance standards.

NexGuard · Monitoring — 367 checks per SAP system
Availability and processesInstances, work processes, RFC reachability, database connection – measured every minute.
Jobs, spool and locksCancelled jobs, backlogs in print queues, lock entries, long-running transactions.
InterfacesStuck queues and failed handovers between systems – before the business notices.
HANA and databaseData and log backups with the age of the last one, disk usage, log volumes, replication, out-of-memory events.
PerformanceCPU, response times, memory and swap – with history from 4 hours to 30 days and thresholds per system.
CertificatesExpiry dates of SSL and SNC certificates – with an alert before they lapse. Public TLS certificates are being shortened step by step to 47 days by 2029.
Beyond SAPLinux servers (104 checks) and Windows (67) as well as SAP cloud services: Cloud Connector, BTP, CPI.
NexShield · Security — six check areas
SAP identityStandard users (SAP*, DDIC) across all clients, password rules, dialog accounts that should not be dialog accounts.
HardeningProfile parameters compared against the baseline, gateway and message server ACLs, transport configuration.
AuthorisationsSAP_ALL and SAP_NEW assignments, critical combinations, RFC destinations with stored passwords of privileged users.
Security audit logWhether it runs at all, what it records – and unusual events, such as series of failed logons from outside.
Vulnerabilities (CVE)Daily comparison of OS packages and kernels against known gaps; ordered by real-world risk (KEV, EPSS), not just by score.
Change recordsWho changed what in the configuration – documented in a form an audit accepts.
Compliance — 14 standards in one catalogue
Germany
KRITIS (BSIG)BSI IT-GrundschutzB3S Medizinische Versorgung§ 391 SGB VDSAG-Prüfleitfaden S/4HANA
European Union
NIS2GDPR – technical measures (TOM)
Poland
KSC (uKSC)KNF Rekomendacja DKRI
International
ISO 27001

One piece of evidence counts towards several standards: a control measured once feeds every standard that requires it. For each control the state is visible – proven, open or not measured.

How it works

Your business data stays with you. The agent only calls out.

On your sideYour systems + agent

The agent reads SAP, HANA and the operating system. Read-only, under your control, with the source code available to you.

In the EUNexControl platform

Analyses, keeps the history and compares daily against known vulnerabilities. Data centre in the EU.

Your teamDashboard + alerts

Sees the state live, receives alerts by e-mail or Microsoft Teams with a concrete recommendation – and reports with evidence.

What travels are measurements and configuration states – no business data, no passwords.

Setup

Installed in an afternoon.

One agent per SAP system, installed on the application server.

Step 01 · 5 minutes

Create access

You receive your access and generate a token for the agent in the dashboard.

Step 02 · 30 minutes

Install the agent

One package, one command on the SAP server. Your Basis team creates the read-only users from our templates – or we do it together.

Step 03 · 60 seconds

See data

System, database and host appear in the dashboard; the first security scan follows within minutes.

RequirementsA Linux server with outbound HTTPS – that is all the agent needs. We clarify the rest before installation.
HANA on its own serverThe agent reads it over the network. No second agent, no new firewall rule.
Without SAP tooNexControl also monitors plain Linux and Windows servers – patches, services, security.
Buying

Included with our service or available standalone.

With our service

Part of Managed SAP Basis

If we run your SAP operations, NexControl is included at no extra cost. We react to the alerts; you always see the same picture we do.

See the service models
Standalone

As a standalone product

Your team runs operations itself and wants monitoring, security and evidence from one set of data: NexControl is also available on its own, licensed by system count and scope. If you need support later, we already know your systems.

Ask for pricing
Common questions

What customers want to know before starting.

Our HANA runs on its own server – two agents?No. One agent on the SAP application server reads the HANA over the network.
Does this work with RISE or a hosting provider?With a hoster or in the cloud the agent runs on the application server as usual. Under RISE, SAP operates the OS and database itself – our agent then runs on a server of yours and checks the application layer via RFC: jobs, interfaces, performance, authorisations, security.
What happens when an alert fires?With our service we react within the agreed time. Without it, your team receives the message – by e-mail or Microsoft Teams – with the cause, the affected system and the concrete next step.
Does Nexbase see our data?Only the measurements of your systems, and only if you have engaged us. Business data never leaves your system.
How do we get out again?Uninstall the agent (three commands) and your access is deleted. Export your reports as PDF beforehand.

See NexControl on your own systems.

Half an hour with your test system and real data – afterwards you know whether it fits. Book a demo →