
SAP security & NIS2
SAP security with evidence that holds up in an audit.
Unlocked standard users, gateways without ACLs, disabled audit logs and outdated packages are findings present in most landscapes. We find them continuously, rank them by real-world risk and document the remediation as evidence for NIS2, ISO 27001 and local regulations.
What we check
Four layers, checked continuously.
HardeningStandard users, gateway and message server ACLs, profile parameters compared against the baseline, password rules.
AuthorisationsSAP_ALL assignments, critical combinations, RFC destinations with stored passwords of privileged users.
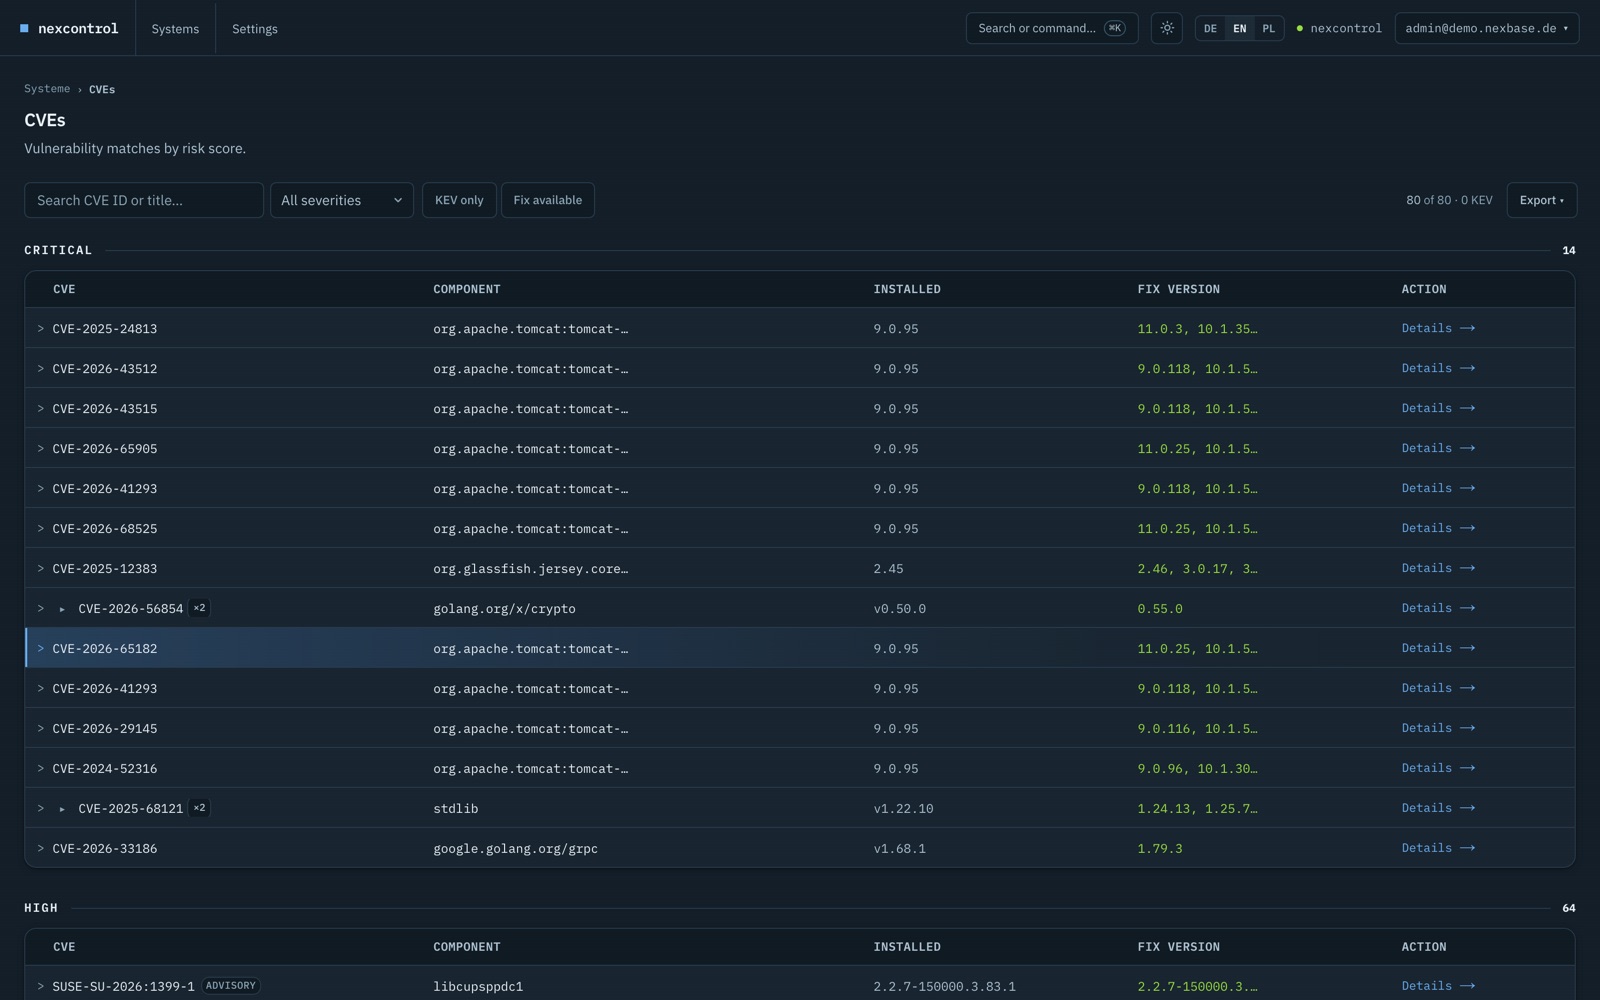
VulnerabilitiesDaily comparison of installed packages and kernels against known CVEs; the most critical first.
LoggingSecurity audit log configuration and unusual events, such as logon attacks from outside.
Common questions
Honest answers to the usual questions.
Does NIS2 even apply to us?That is for your legal team or security officer to decide. We deliver the technical part: checks, remediation and the evidence.
Do you also run penetration tests?No. We check configuration, authorisations and known vulnerabilities – continuously rather than once a year. A pentest complements that; it does not replace it.
How fast do we see first results?The first scan delivers a prioritised list on the day the agent is installed.
Who fixes the findings?Your team, using the instructions attached to every finding – or we do, if the systems are under our service.
The first scan shows where you stand.
We install the agent, measure for a day and discuss the result with you. Then you decide how to proceed. Ask for a scan →